A technology company of about 400 people had AI spreading across cloud platforms, code repositories, identity systems and model providers.
The basic questions had no consistent answer. Which AI systems were running. Who owned them. What data each one could reach. Which had been reviewed, and what still needed fixing. The company had security tools. What it did not have was one layer built for AI specifically.
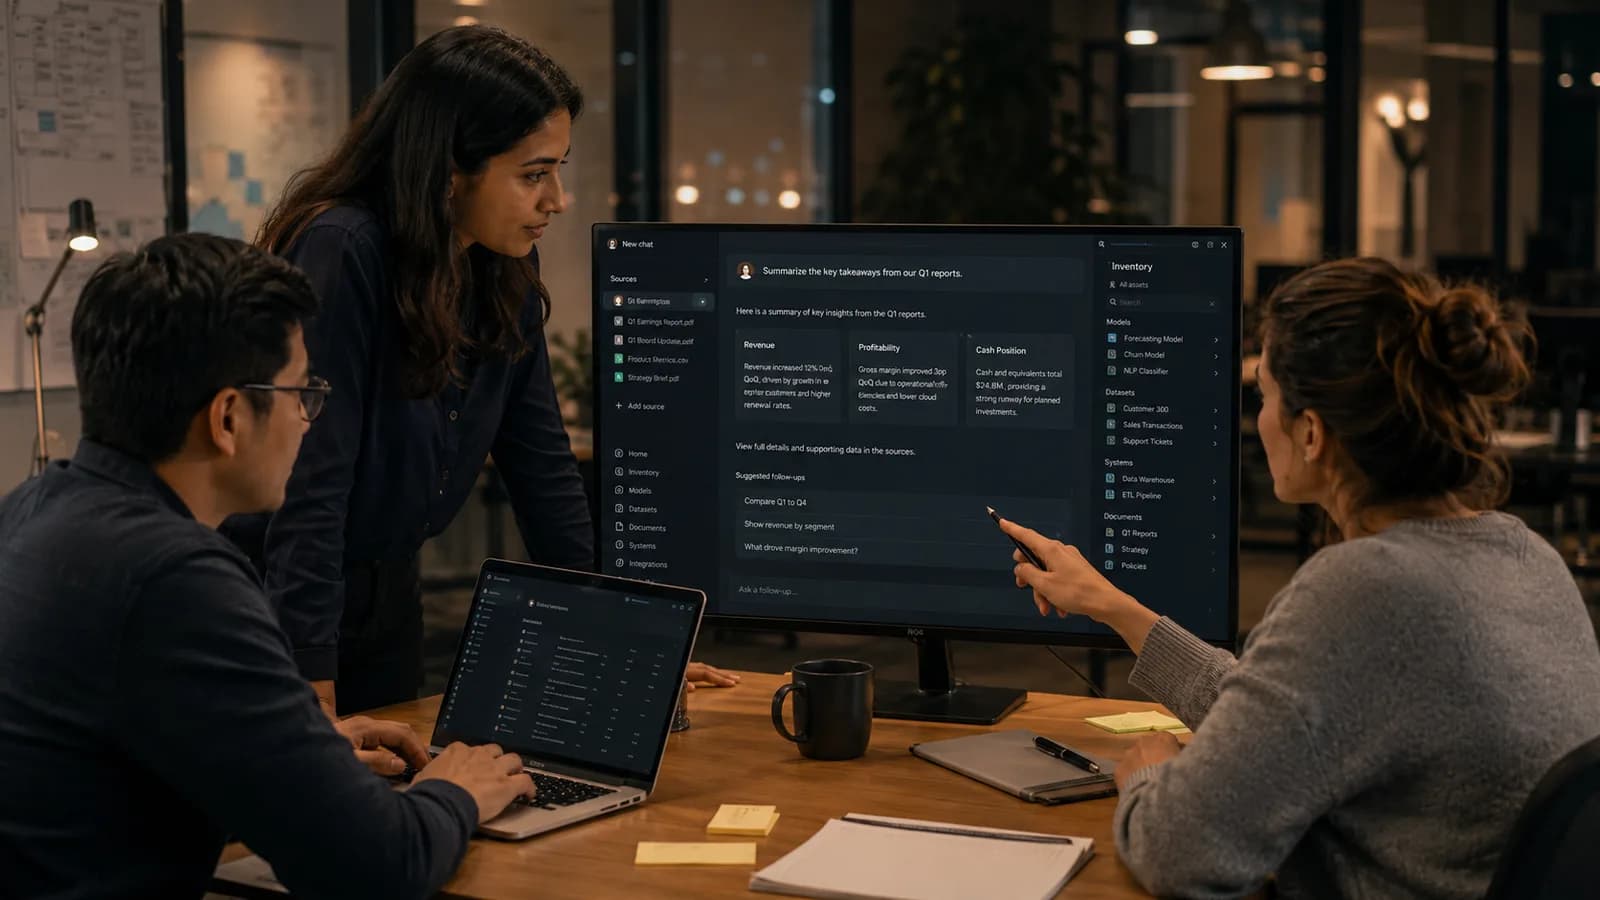
An AI security and posture system built around the company's own environment and governance requirements rather than configured from a template. It discovers AI-related assets and activity, assesses risk, and carries the review workflow from request through to sign-off.
We built it for the company's internal use.
Security gained one place to see which AI systems exist, who owns them, and what they can reach.
Before that, AI activity sat across separate systems and teams, so answering an ownership or access question meant asking around and hoping the answer was current.
The first release did not cover everything. A complete ownership model, formal intake and registration, deeper model and dataset scanning, and several platform integrations were left for a later release rather than shipped half-built.
Industry
Technology
Size
About 400 employees
Region
North America
Focus
AI system discovery, governance and control
Deployment style
Custom build for internal use