A healthcare organization in the United States had AI spreading across internal applications, cloud services, identity systems and external model providers, with no dependable inventory of what existed or who owned it.
Visibility was only half the problem. In healthcare, every AI system also has to be checked against sensitive-data boundaries, access controls and the organization's own governance rules, and there was no consistent way to do that.
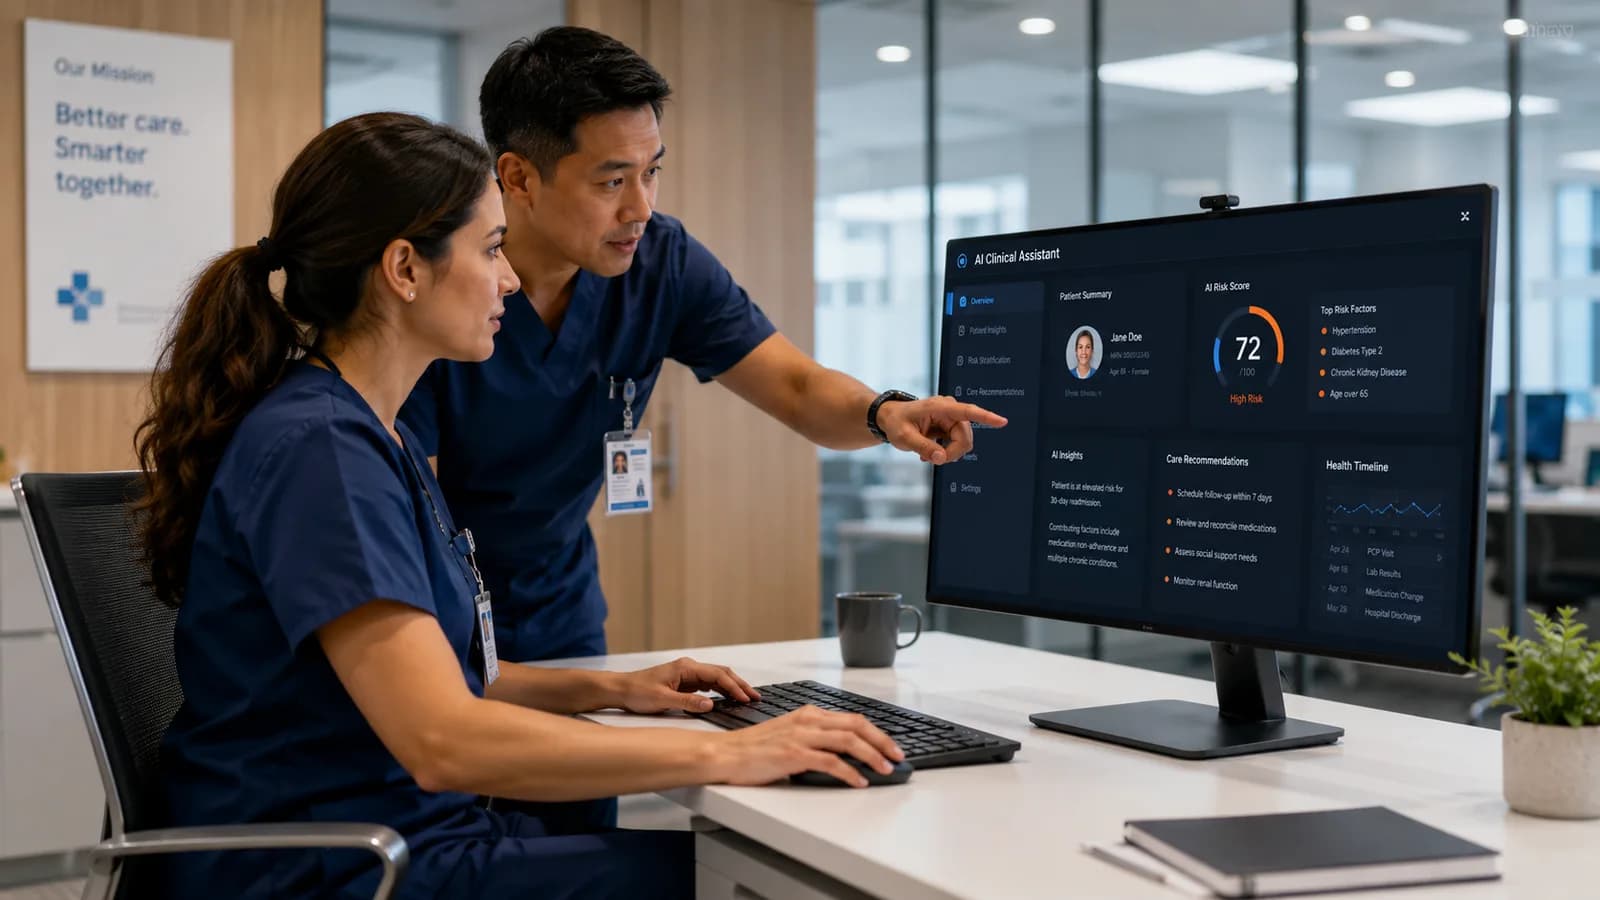
An AI security and posture system built around the organization's environment and its governance requirements. It discovers AI-related assets and activity, records ownership, assesses risk and posture, and shows what each system can reach.
We built it for the organization's internal use.
The organization could see which AI systems touched sensitive information, and check each one against its own governance rules.
Before that, the inventory was incomplete and the checks were done case by case, so the same question could get a different answer depending on who asked it.
The first release did not cover everything. Formal intake and registration, deeper model and dataset scanning, and several platform integrations were left for a later release rather than shipped half-built.
Industry
Healthcare
Size
About 900 employees
Region
United States
Focus
AI discovery, ownership and governance
Deployment style
Custom build for internal use