A financial institution in Canada had teams adopting AI across cloud infrastructure, internal applications, repositories and external model services.
The existing security and asset tools captured parts of the estate but gave no single operating model for AI. That left basic accountability questions unanswered: which systems were active, which business or technical owner was responsible for each, what information each could reach, and what risks were still open.
An AI security and posture system built around the institution's environment, combining discovery, ownership, posture assessment, access visibility, runtime control and remediation tracking in one place.
We built it for the institution's internal use, so AI could be managed as an operating environment rather than a collection of separate pilots.
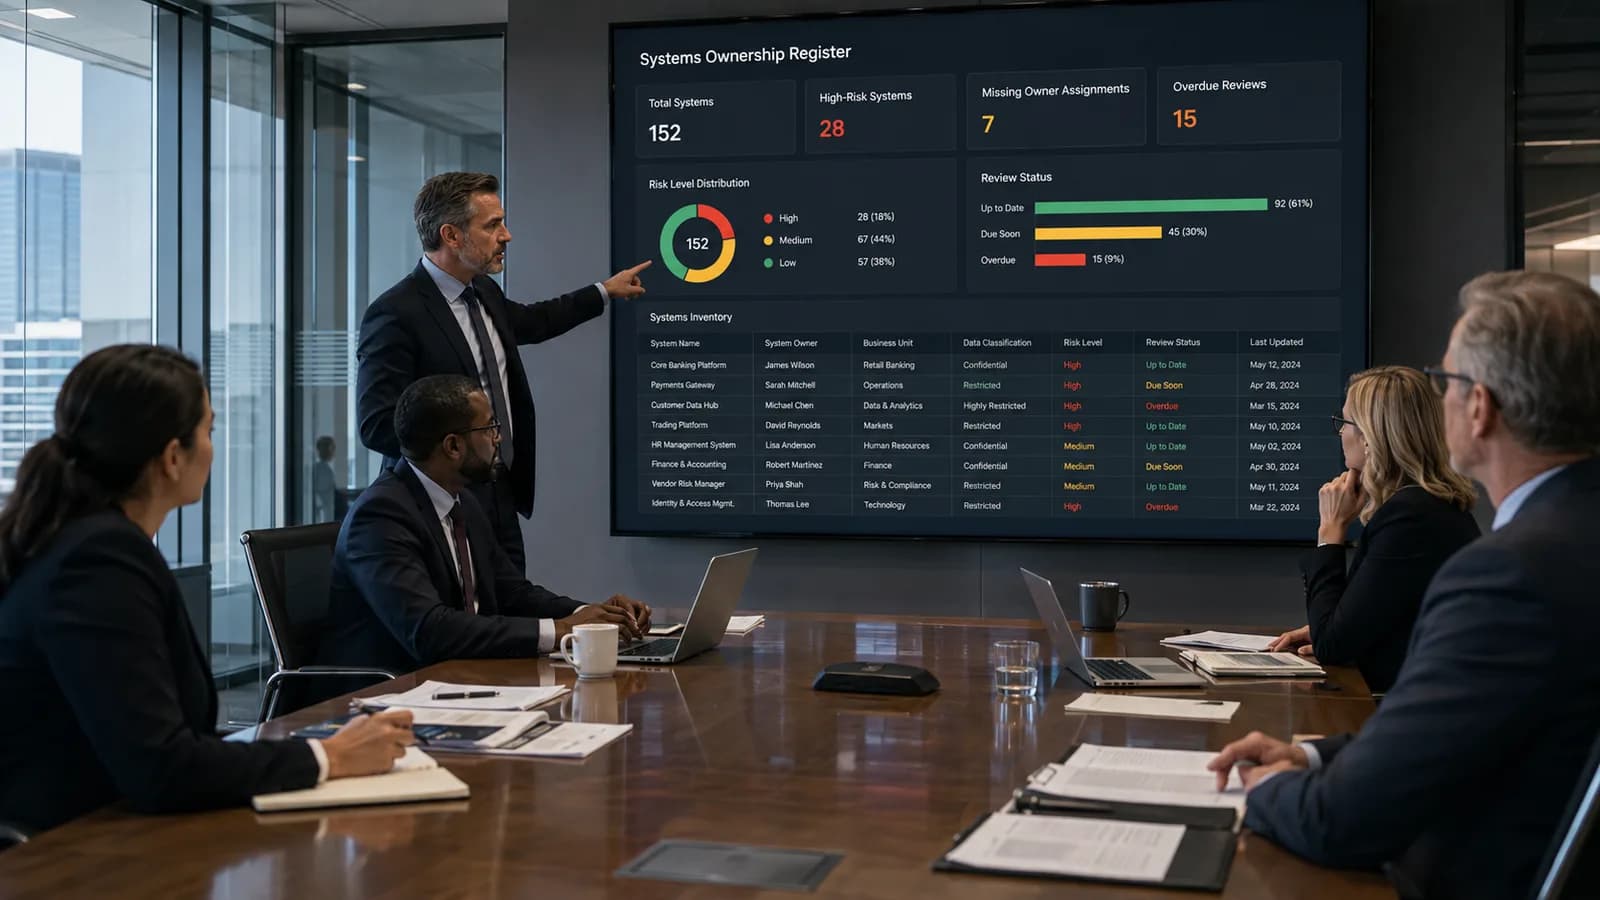
Every AI system got a named owner, and the security team had one register to see them all in.
Before that, accountability was spread across teams and tools, so establishing who was responsible for a given system took a round of asking.
The first release did not cover the whole estate. Formal intake, deeper access-governance depth and several platform integrations were left for a later release rather than shipped half-built.
Industry
Financial services
Size
About 1,200 employees
Region
Canada
Focus
AI ownership, review and remediation
Deployment style
Custom build for internal use